Build your logic.
Not your bank connection.
Not your bank connection.
Building your own cashflow tool with vibe coding? Good idea — build the part that makes you special.
Bank data, forecast and permissions come from COMMITLY: via API and MCP, without your own contract with a bank data provider.


Building is fast.
Operating is not.
Operating is not.
With AI, a tool is built in a weekend. “Built in a weekend” still turns into “maintained every week” — because the operating stays with you:
Provider contract & onboarding
Your own contract with a bank data provider: onboarding, data processing agreement, running costs from the first account — and dependence on exactly one provider.
Renewing bank consents
PSD2 consents expire and want renewing regularly — for every account, again and again. If the chain breaks, bookings go missing from your forecast.
Encryption & keys
Encrypting financial data is not enough — the keys want managing, rotating, and swapping fast when a vulnerability hits.
Backups with restore
A backup only counts once the restore is tested. Regularly, documented — including in the week when nobody has time.
GDPR & retention
GDPR documentation, the 72-hour breach notification deadline and the commercial and tax retention obligations — paperwork with deadlines.
Updates & scaling
Security updates, bugfixing, growth: every dependency in your stack ages — and locally built solutions hit their limits fast.
“A cashflow plan only one person understands is not an asset. It is a risk with bank access.”
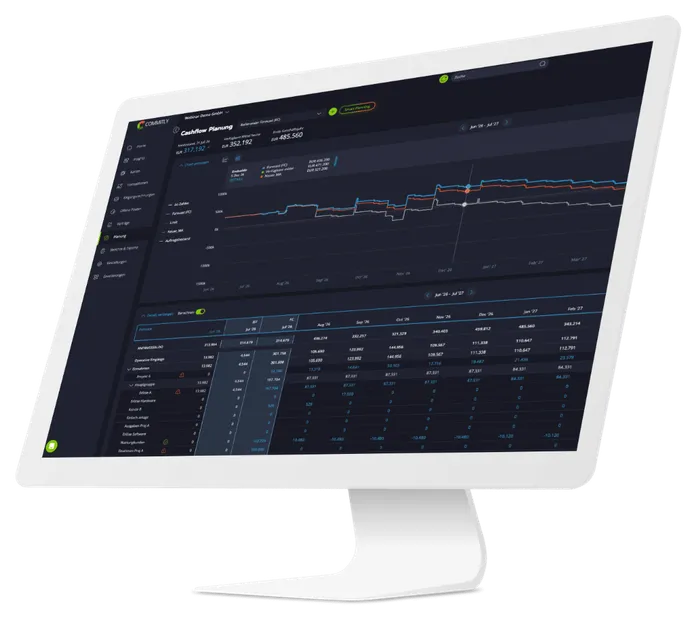
Bank data via API — regulated, hosted, maintained
COMMITLY connects over 5,000 banks across Europe, via PSD2 and EBICS — through several regulated aggregators: if one provider's connection to a bank fails, another can step in. You simply dock on.
- REST API following OpenAPI 3.1 — documentation at developer.commitly.com
- MCP Server for your AI assistant, hosted by COMMITLY
- Hosted in Germany, ISO 27001:2022 certified
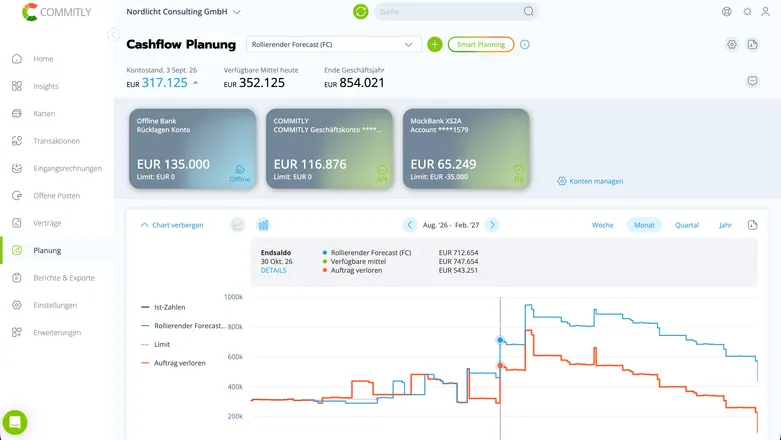
More than account data: the planning is already done
A plain banking API delivers bookings — the planning layer you build yourself. In COMMITLY it is finished and available via API and MCP, calculated with the direct method (IAS 7) and thus fit for bank and auditor conversations.
- AI categorisation and forecast — from bank data, open items and plan values
- Scenarios and plan-actual comparison — side by side instead of file copies
- Consolidation, roles and permissions — several entities, one state
Your AI asks COMMITLY. Your app stays lean.
Instead of building your own database and analysis logic, Claude or ChatGPT queries the prepared data via MCP directly in COMMITLY — with the same permissions as a person. Your app only handles what makes it special.
- No analysis layer of your own — forecast and scenarios come back ready
- Permissions down to category level — for the language model, too
- Model-independent — Claude, ChatGPT, Mistral or a model of your own
Build it — or build on it?
The honest comparison — not build cost versus licence, but what comes afterwards.
| Self-built | COMMITLY | Hybrid (COMMITLY + your app) | |
|---|---|---|---|
| Bank access | Your own contract with a bank data provider: onboarding, DPA, costs from the first account | Over 5,000 banks via PSD2 and EBICS, through several regulated aggregators — included in the price | Comes from COMMITLY — no provider contract of your own |
| Running costs | Aggregator, hosting, database, monitoring — plus your time, every week | One edition, one price — predictable and cancellable monthly | Edition plus your own hosting — for your logic only |
| Operations & security | Encryption, backups with restore, GDPR, 72-hour breach deadline, updates — all on you | Operated by COMMITLY: hosted in Germany, ISO 27001:2022 | The regulated stack sits with COMMITLY, your app stays lean |
| Planning logic | Forecast, scenarios, plan-actual, consolidation — you build and maintain it yourself | Ready: AI categorisation, forecast, scenarios, plan-actual, consolidation — direct method (IAS 7) | Ready from COMMITLY, available via API and MCP |
| Permissions & auditability | A file or database is all-or-nothing — roles and audit trail you build yourself | Roles down to category level, approvals, audit trail | Permissions and audit trail stay in COMMITLY — for your app, too |
| Support & responsibility | Several providers pointing at each other when something breaks — you are the one responsible | One contact, one contract, one responsible party | One for the stack — your logic stays with you |
| Dependence on one person | The planning hangs on the person who built it — if they drop out, the planning drops out | A shared application instead of a file: several people, one state, handover-ready | The foundation is handover-ready — only your logic needs documentation |
Honestly: when self-building is enough
If it is about a single bank with its own API, with no planning logic and no team, a self-build is perfectly fine. This page is for everyone whose weekend project is turning into a system with responsibility.
The price anchor
Business Edition EUR 105 per month including the direct API; AI Connect (MCP Server) as an add-on for EUR 15 per month — included in Professional. All details on the pricing page.

Ready for your cash flow platform?
Questions and answers
about self-building
Technically yes, and bank access is not the obstacle: regulated aggregators sell PSD2 account access as a service, so you do not need a licence of your own. COMMITLY connects banks the same way. What you buy along with it, though, is a provider contract with onboarding, a data processing agreement, running costs from the very first account and dependence on one provider. And what you get is account data — forecast, plan vs. actual, scenarios and consolidation are things you build yourself. On top of that comes running it: encryption, key management, roles and permissions, audit trail, backup with a tested restore, patching when vulnerabilities appear, GDPR documentation, the 72-hour notification deadline for data breaches and the retention obligations under commercial and tax law. Every one of those is solvable. Together they are not a building job, they are a permanent one.